

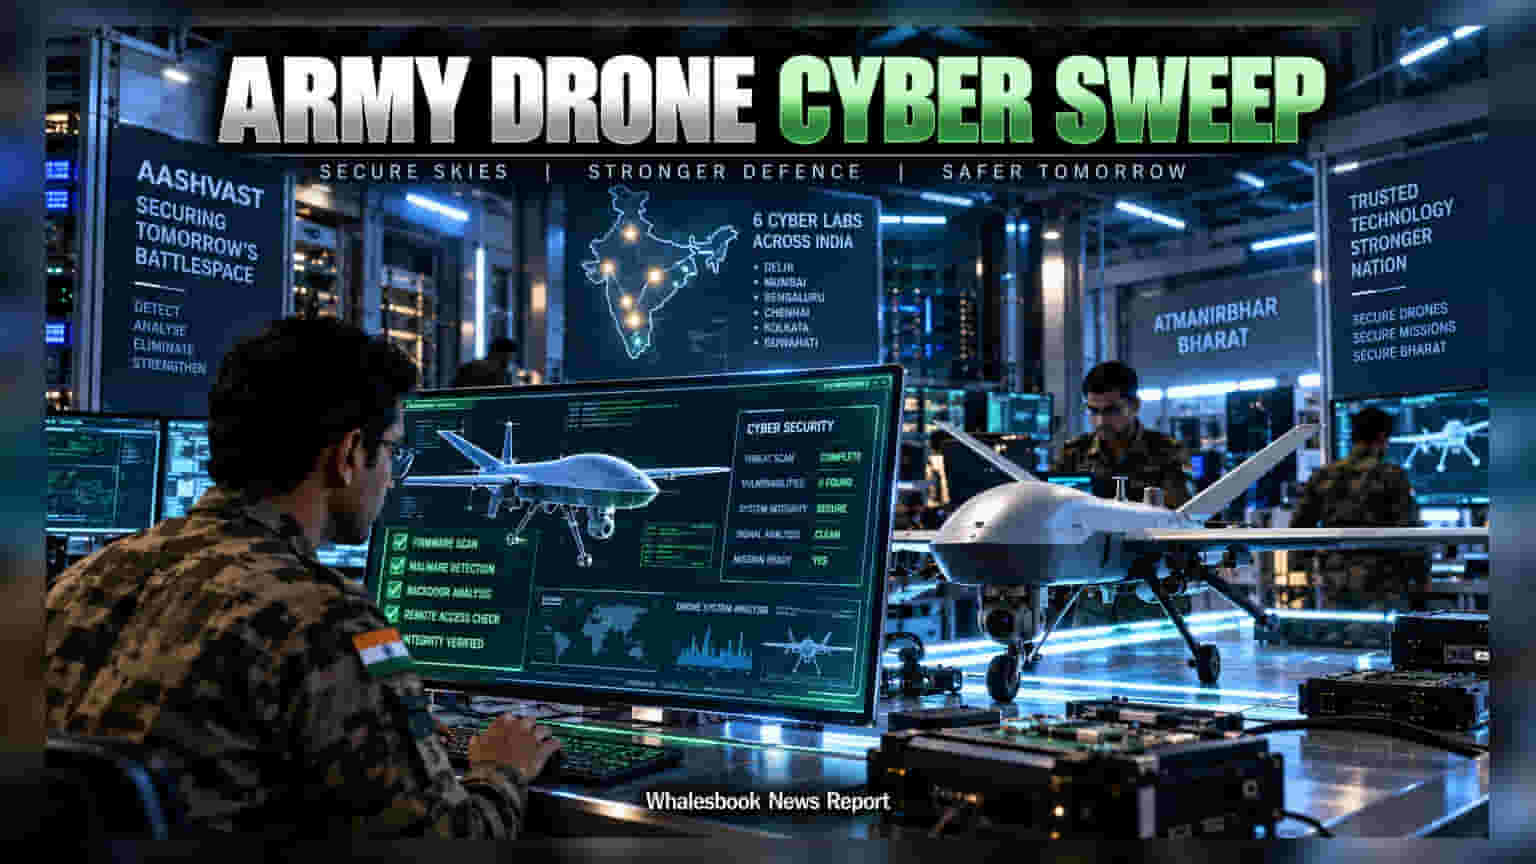
The Indian Army has established six specialized laboratories under the AASHVAST initiative to scan military drones for malicious firmware and foreign-origin vulnerabilities. This security push highlights the military's shift toward stricter hardware verification, a trend that is likely to influence future defense procurement standards and domestic manufacturing requirements.
The Indian Army has launched the AASHVAST initiative, deploying six specialized cyber laboratories across the country to strengthen the security of its drone fleet. The primary objective of these facilities is to identify and remove malicious firmware and potential backdoors in military electronics, particularly those of foreign origin. The first of these laboratories is already operational in Delhi, marking a structural change in how the defense force handles supply chain security.
Targeting Supply Chain Vulnerabilities
The initiative addresses a critical security concern: the risk of remote interference or hijacking of tactical unmanned aerial vehicles. These cyber laboratories are designed to scan components for approximately 14 types of vulnerabilities, including unauthorized remote-access tools, time-delayed faults, and location-based triggers. By moving beyond physical inspection to deep-level firmware and embedded system analysis, the Army is aiming to eliminate single points of failure in its operational equipment.
The development of AASHVAST, attributed to QuickPay Pvt Ltd for the Directorate General of Electronics and Mechanical Engineers, reflects a broader shift toward software-driven defense. The project is expected to expand its scope beyond drones to include other sensitive electronics, such as CCTV systems, in the coming phases.
Impact on Defense Indigenization
For investors and companies in the defense sector, this move is a clear signal of the intensifying focus on technological self-reliance under the Atmanirbhar Bharat policy. The Ministry of Defence has already issued several 'positive indigenization lists' that restrict the import of various defense equipment to encourage local manufacturing. This new focus on firmware security suggests that defense contracts will increasingly prioritize vendors who can guarantee the integrity of their supply chains and demonstrate indigenous capabilities.
While this initiative enhances national security, it also introduces operational changes for defense manufacturers. Companies supplying the defense sector may need to invest more in indigenous technology and secure software development to meet these higher compliance standards. Increased scrutiny on components could lead to longer procurement timelines or higher costs for equipment that does not meet these stringent validation protocols.
What Investors Should Track
The long-term impact of this initiative will be visible in the procurement policies of the Ministry of Defence. Investors may monitor whether these security protocols become a standard requirement for private defense contractors and public sector undertakings. Additionally, any updates on the rollout of these validation protocols to other electronic categories, such as communication equipment or surveillance systems, will be important for understanding the addressable market for domestic hardware security firms. The core monitorable remains how rapidly the industry can adapt to these security-first procurement requirements without significant disruptions to project timelines.